 Featured
$49
Ethical Hacking & Pentesting
Ethical Hacking from Scratch
Zero to practical offensive security: lab setup, discovery, exploitation and post-exploitation.
Short video lessons and hands-on labs take you from beginner to job-ready — ethical hacking, bug bounty, web security and more.
Hack The Planet exists for one reason: to take you from curious beginner to confident, job-ready cybersecurity practitioner — through short video lessons and real hands-on practice, in the languages you actually speak.
Short, hands-on video lessons across ethical hacking, bug bounty, web and network security.
Guided labs and exercises with every course — learn by doing, not just watching.
Curated course bundles with 1-on-1 mentorship for focused career tracks.
Direct access to mentors on WhatsApp for questions about courses and enrollment.
Hand-picked starting points from the catalog — practical, lab-based, and mentor-supported. The full catalog of 49 courses lives on the courses page.
Featured
$49
Ethical Hacking & Pentesting
Zero to practical offensive security: lab setup, discovery, exploitation and post-exploitation.
 Featured
$35
Ethical Hacking & Pentesting
Modern web exploitation: SQLi, XSS, SSRF, RCE and filter bypasses in hands-on labs.
 Featured
$39
Ethical Hacking & Pentesting
Recon automation, business-logic flaws and professional vulnerability reporting.
 Featured
$29
Ethical Hacking & Pentesting
HTTP/HTTPS, misconfigurations, CMS and multi-tier web application pentesting.
 Featured
$35
Ethical Hacking & Pentesting
Threats, vulnerabilities, cryptography and network defense fundamentals.
 Featured
$29
Ethical Hacking & Pentesting
Passive and active recon, subdomain enumeration, port profiling and footprinting.
 Featured
$25
Ethical Hacking & Pentesting
Onion routing, hidden services and safe OSINT workflows for analysts.
 Featured
$39
Ethical Hacking & Pentesting
Scanning, enumeration, exploitation and defense baselines. Highly recommended starting point.
Looking for a specific course or dedicated lab access? Contact us and we will arrange it for you.
Contact UsAuthorized web proxy testing, modern web attacks and comprehensive web pentesting — pair these courses with hands-on labs from PortSwigger Web Security Academy.
Featured
$35
Ethical Hacking & Pentesting
Modern web exploitation: SQLi, XSS, SSRF, RCE and filter bypasses in hands-on labs.
Featured
$29
Ethical Hacking & Pentesting
HTTP/HTTPS, misconfigurations, CMS and multi-tier web application pentesting.
 $19
Ethical Hacking & Pentesting
Authorized-scope web proxy testing: parameters, access control and CSRF.
Complete learning paths that take you from fundamentals to job-ready skills.
6 Months track
The most popular route into cybersecurity — fundamentals, Linux and SOC basics with 1-on-1 mentorship.
Includes 1-on-1 mentorship and lab access
8 Months track
Full offensive track — web hacking, bug bounty hunting and professional reporting with 1-on-1 mentorship.
Includes 1-on-1 mentorship and lab access
6 Months track
High-demand skills — AI security, cloud and automation with priority mentorship.
Includes 1-on-1 mentorship and lab access
Practical cybersecurity training through short, hands-on video lessons and real lab practice. And yes — “Palnte” in our name and web address is deliberate: it is our own spelling of “Planet”, and the name our students know us by. This is the official Hack The Planet website.
Hack The Planet started with one goal: make practical cybersecurity education accessible to everyone. No fluff, no thousand-slide decks — just short, hands-on video lessons built from real-world practice.
To take learners from complete beginners to confident, job-ready defenders and ethical hackers through learning by doing — in the languages our learners actually speak.
A world where anyone with curiosity and discipline can build a career in cybersecurity — guided by principled ethical hackers who learned their craft the practical way.
I am Abdullah Balouch, a cybersecurity practitioner from Pakistan. I started Hack The Planet to make practical cybersecurity education accessible to everyone — short, hands-on video lessons in Urdu, Hindi and English, built from real-world practice, not just theory.
Through my Telegram channel, I share free resources and course updates with a growing community of learners every day.
Short video lessons plus real labs — the fastest way from beginner to job-ready.
Every concept is paired with guided practice in real lab environments — you build skill, not just theory.
Finish each path with hands-on assessments that mirror real authorized testing and defensive work.
Direct guidance, lab debugging support and career advice from active security practitioners.
Training mapped to the threats teams actually face — OWASP Top 10, ransomware defense and secure coding.
Lessons are refreshed continuously to reflect the 2026 threat landscape, AI tooling and cloud security.
Join a growing community of learners, monthly CTF challenges and a network that shares real security opportunities.
Our Dark Web OSINT training explains how onion services work and how defenders monitor them for threat intelligence — safely, legally and with the right OpSec.
Threat intelligence, defensive security and career guidance from the HTP team — 21 in-depth guides and counting.
 Threat Intelligence
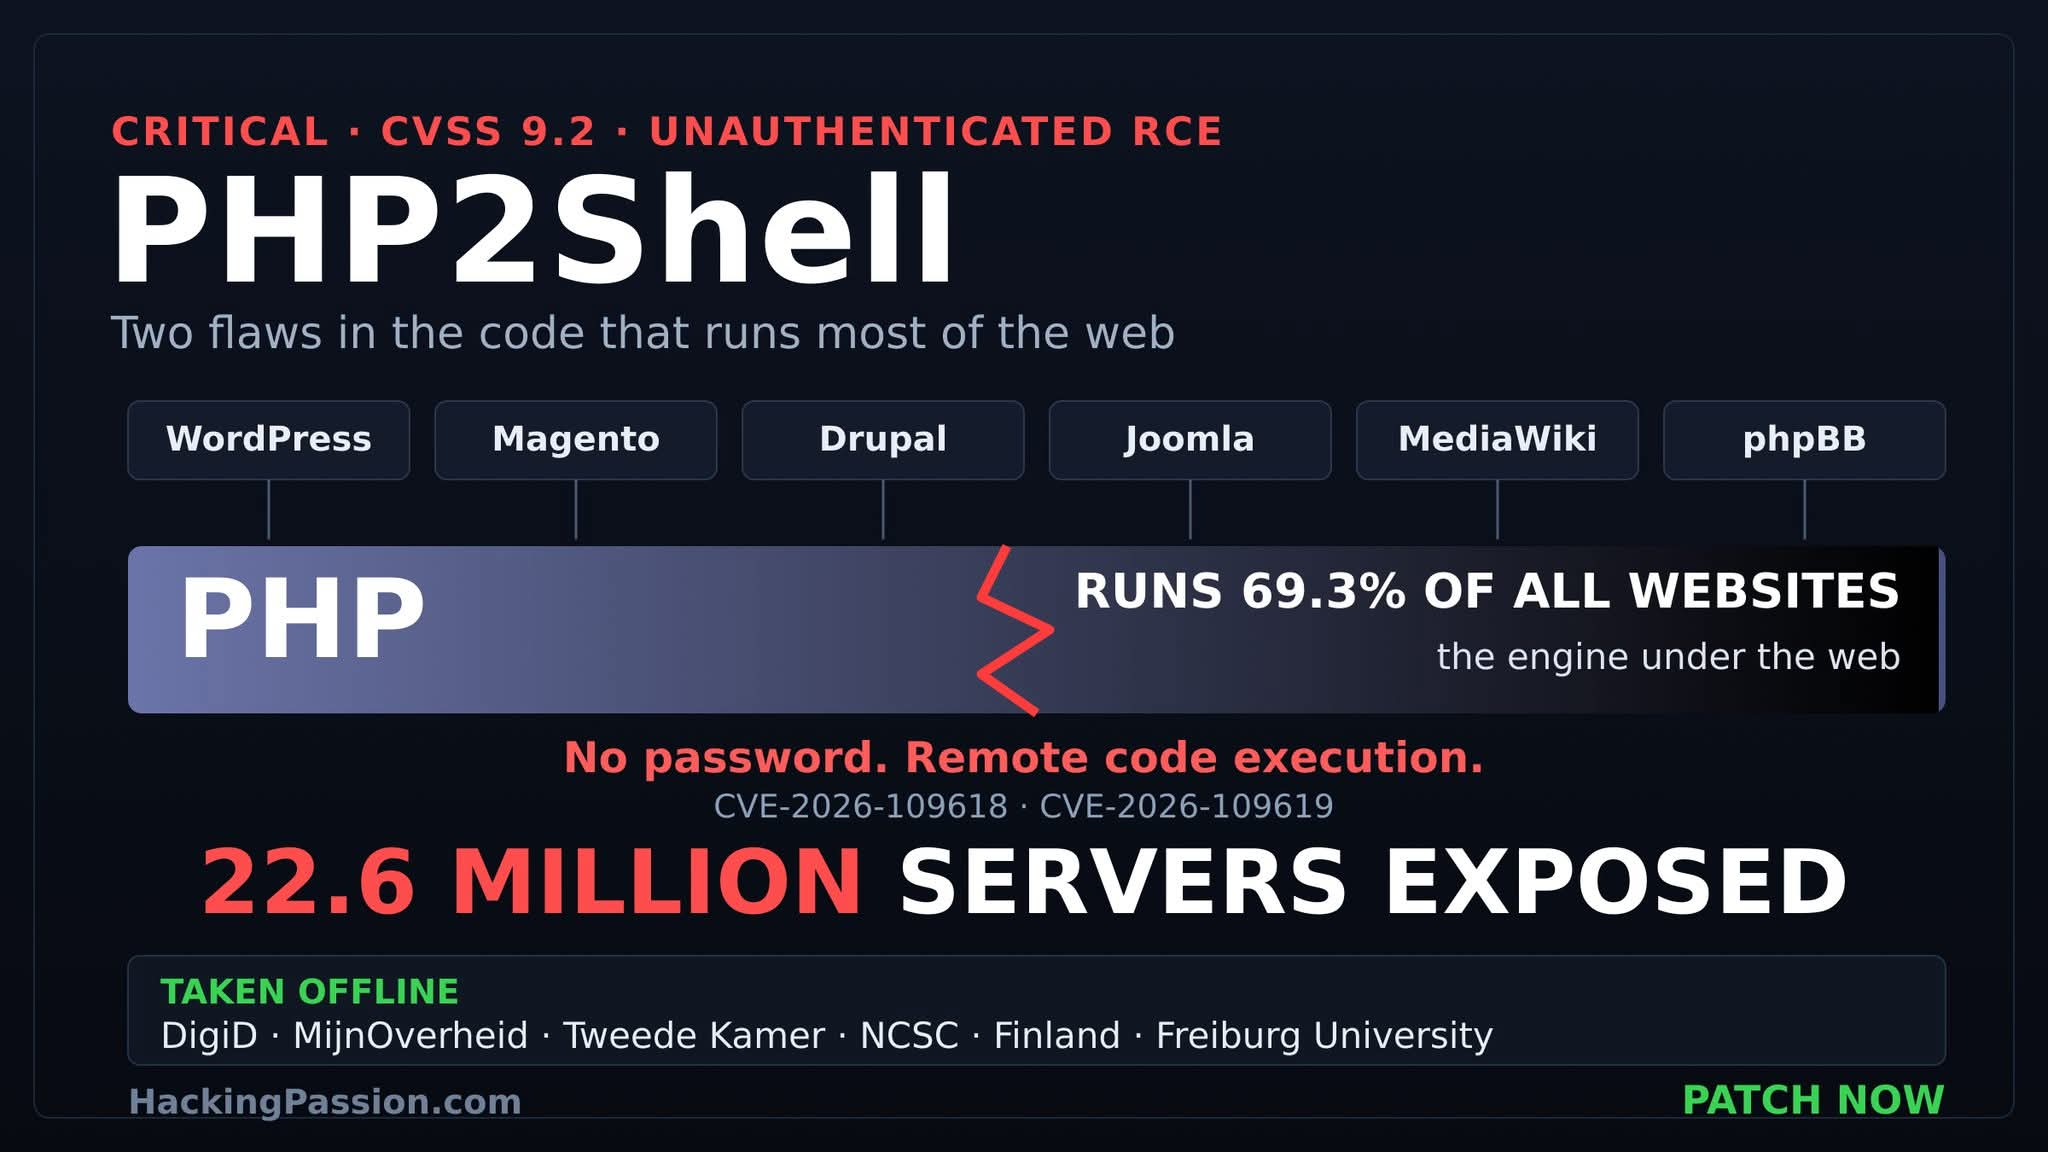
Two critical PHP vulnerabilities — CVE-2026-109618 and CVE-2026-109619, both CVSS 9.2 — allow unauthenticated remote code execution on millions of servers. Governments took national services offline, Cloudflare saw early attacks, and updating WordPress does not fix it. What happened, who is exposed, and what to do right now.
 Threat Intelligence
AI writes phishing emails, hunts vulnerabilities, and clones voices — and it also triages alerts, hunts threats, and patches code. The same technology fights on both sides. Here is what that means for security, and for your career.
 Exploits & Zero-Days
CVE-2021-44228. CVE-2023-23397. These codes appear in every breach headline — but what exactly is a CVE, who assigns it, and how do professionals use the system to decide what to patch first? A complete beginner-friendly guide.